Webhooks guide
Last updated: November 3, 2026
Why webhooks?
Webhooks let you react to a Zuddl activity the moment it happens—no polling, exports, or manual uploads. For example, a prospect registers for your flagship event, requiring you to instantly notify the account owner in Slack or Salesforce. An attendee has modified the hotel check-in date, and that should get synced to the hotel booking app that the client uses to block rooms for the guests. These are some of the many use cases of webhooks in the digital events context.
Overview
A webhook is an HTTPS endpoint that you own to which Zuddl delivers a JSON payload whenever subscribed actions occur. The payload keeps you notified of the action and provides the required details.
An action can be any discrete change in Zuddl, such as registration approved, poll answered, etc.. Actions can be broadly categorized into two types:
Org-level: platform-wide actions such as 'event created'
Event-level: actions within specific events such as 'ticket modified'
Creating a Webhook
Follow the steps mentioned below to create a webhook from your Zuddl dashboard.
Prerequisites
- You must be an Owner or Admin of the Zuddl account
- Have an HTTPS URL ready to receive POST requests
- Generate or copy a token for signature validation on your server
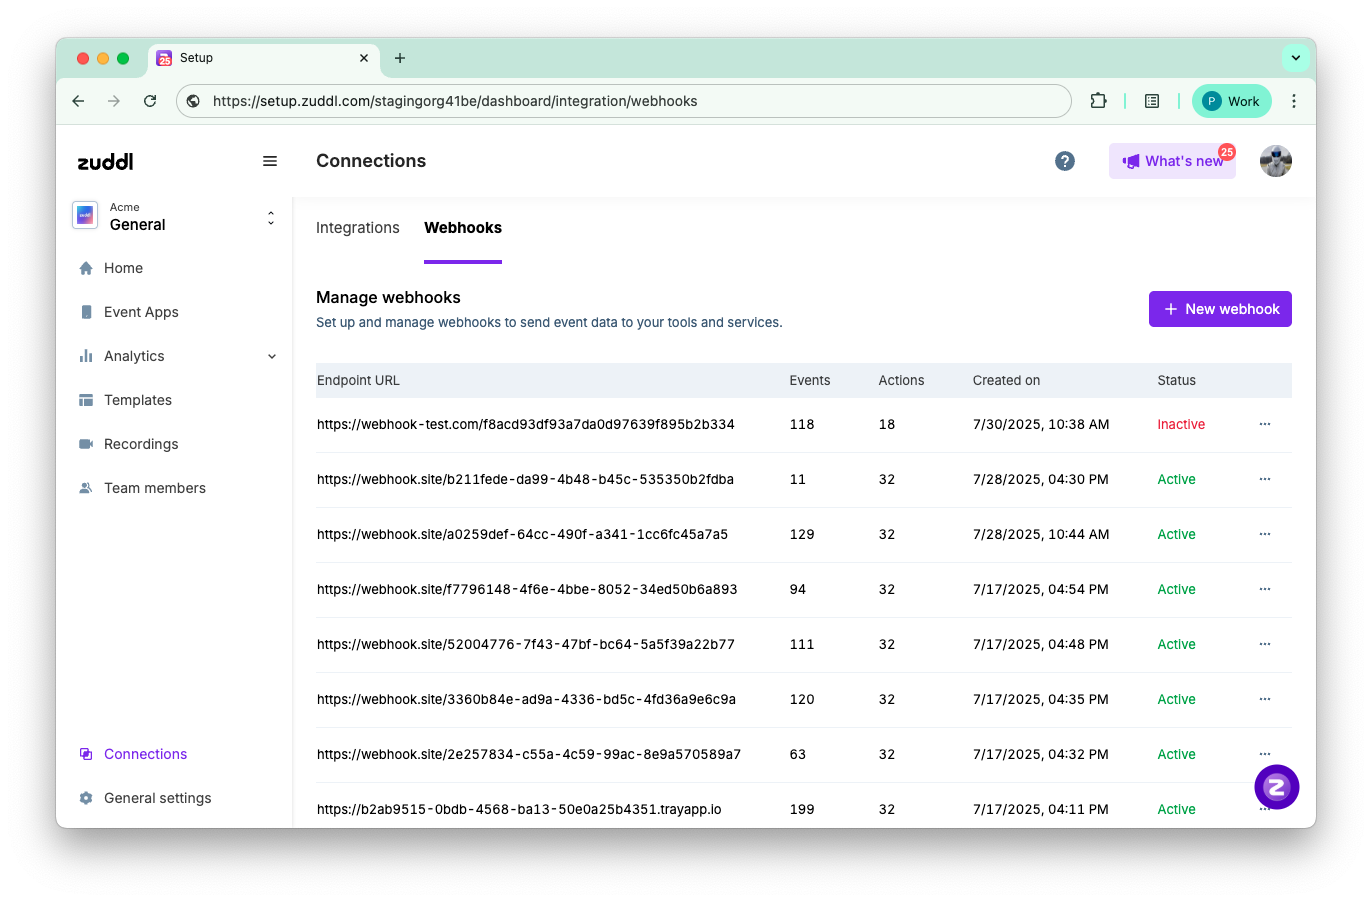
From the Zuddl dashboard, go to Connections → Webhooks tab.
Click New webhook. (You can create up to 20 per org.)
Enter the Endpoint URL. The endpoint URL must start with 'https://.'
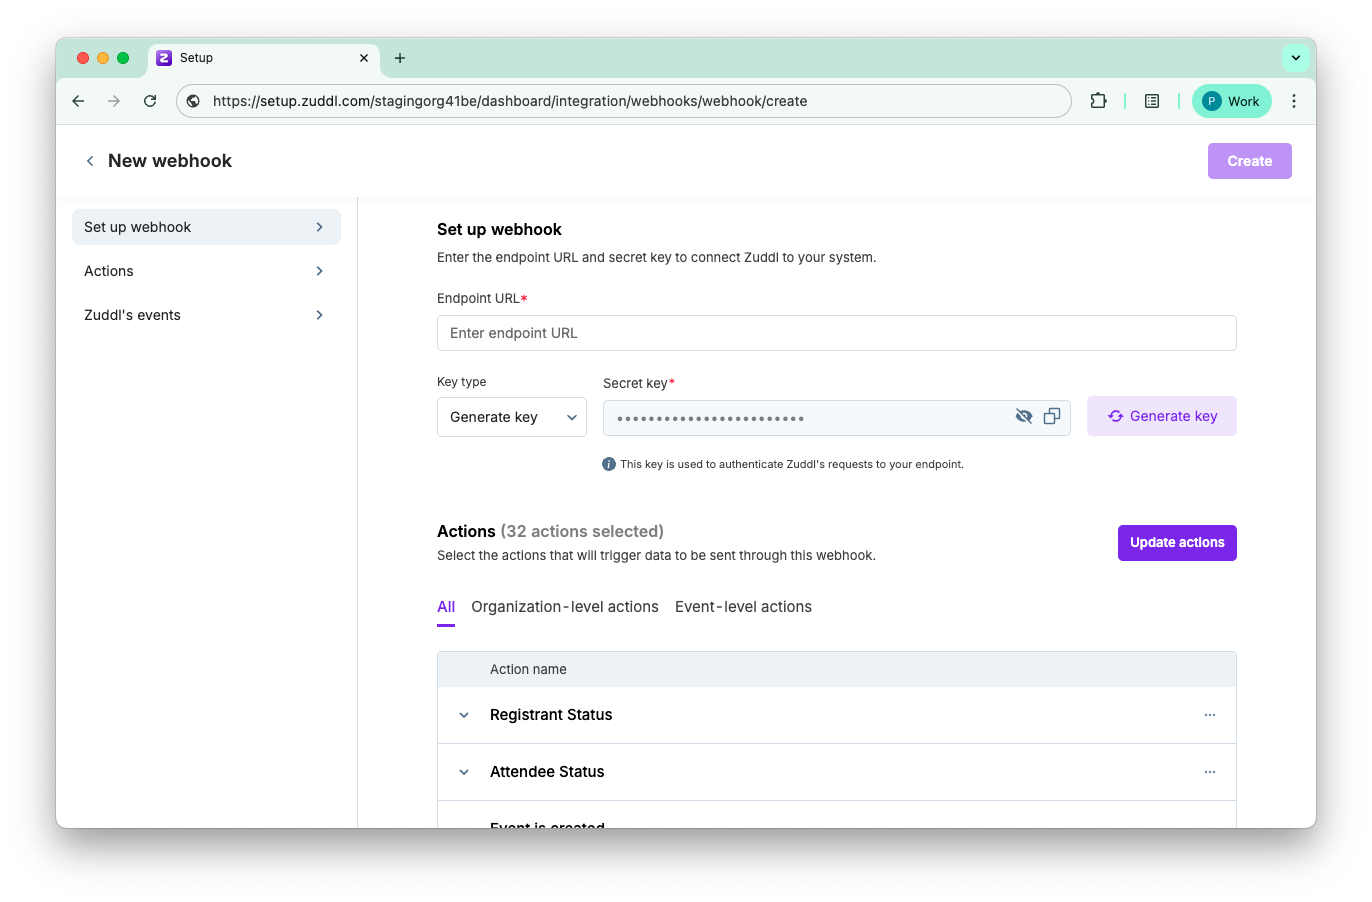
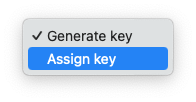
Choose a Key type.
Generate key: System-generated key
Assign key: Custom key
Enter a secret key if Assign key is selected from the previous step. If Generate key is selected, copy-paste the system-generated key.
(Optional) Under Custom headers, click Add header and enter a Header name (e.g.
x-api-key) and a Header value. Repeat for up to 3 headers. To remove a header, click the delete icon next to it.Custom headers are sent with every request from this webhook. Use them to authenticate Zuddl with your endpoint or API gateway (for example
Authorization: Bearer <token>orx-api-key: <key>) without needing a proxy. See Custom headers below for rules.Now, click Update actions to select one or more org-level and/or event-level actions.
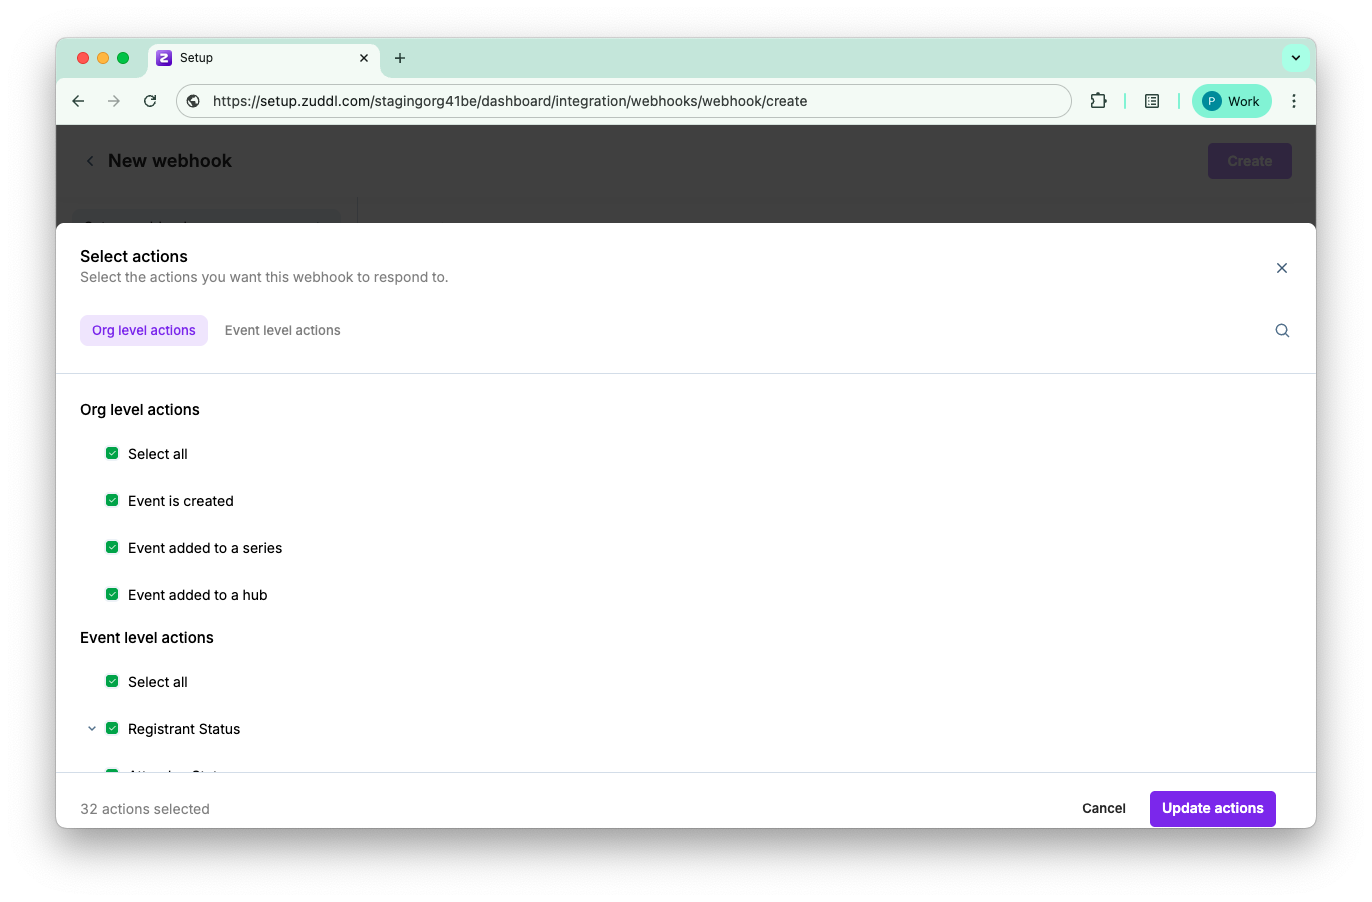
By default all the actions listed here will be selected, you can proceed with all the selected actions or modify the selection and click on Update actions”
Toggle On/Off Automatically include future events.
When ‘On’ in any event type (Webinar, Field events, etc.,) tab, any newly created event of that type will be included automatically in that webhook. The endpoint will receive the data about the subscribed event-specific actions for the newly created event.
When ‘Off” in any event type (Webinar, Field events, etc.,) tab, any newly created event of that type will not be included automatically in that webhook. The endpoint will not receive the data about the subscribed event-specific actions for the newly created event.
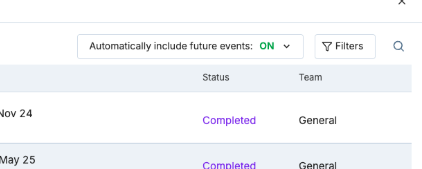
By default, all on-going & upcoming events will be selected
Once actions are selected, click Update actions.
Next, you must select the events for which you need the webhooks to track action. Click the Select events button to select the required events from the list of events in your Zuddl organization.
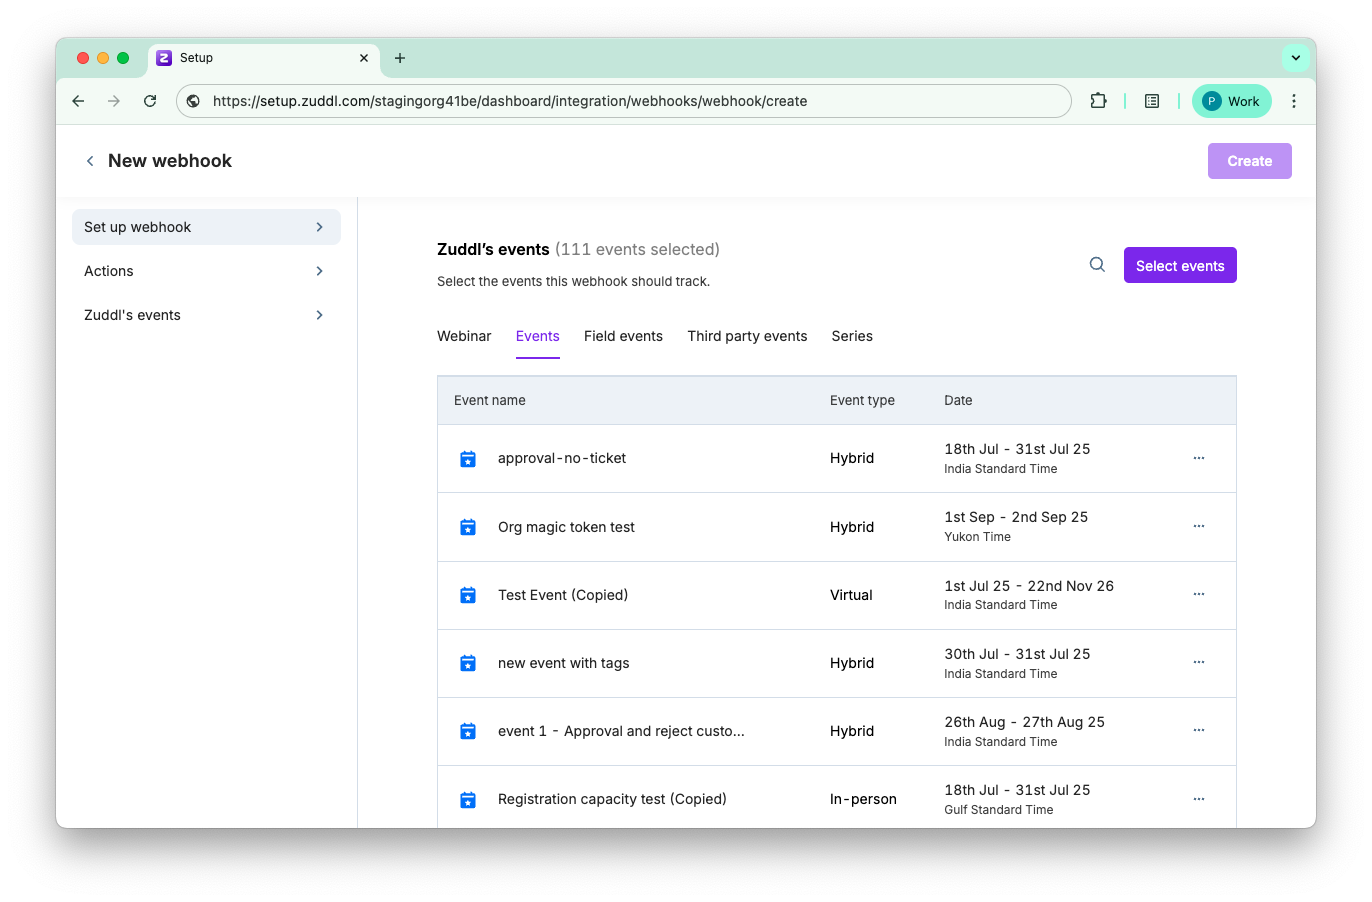
Once selected, click Select events.
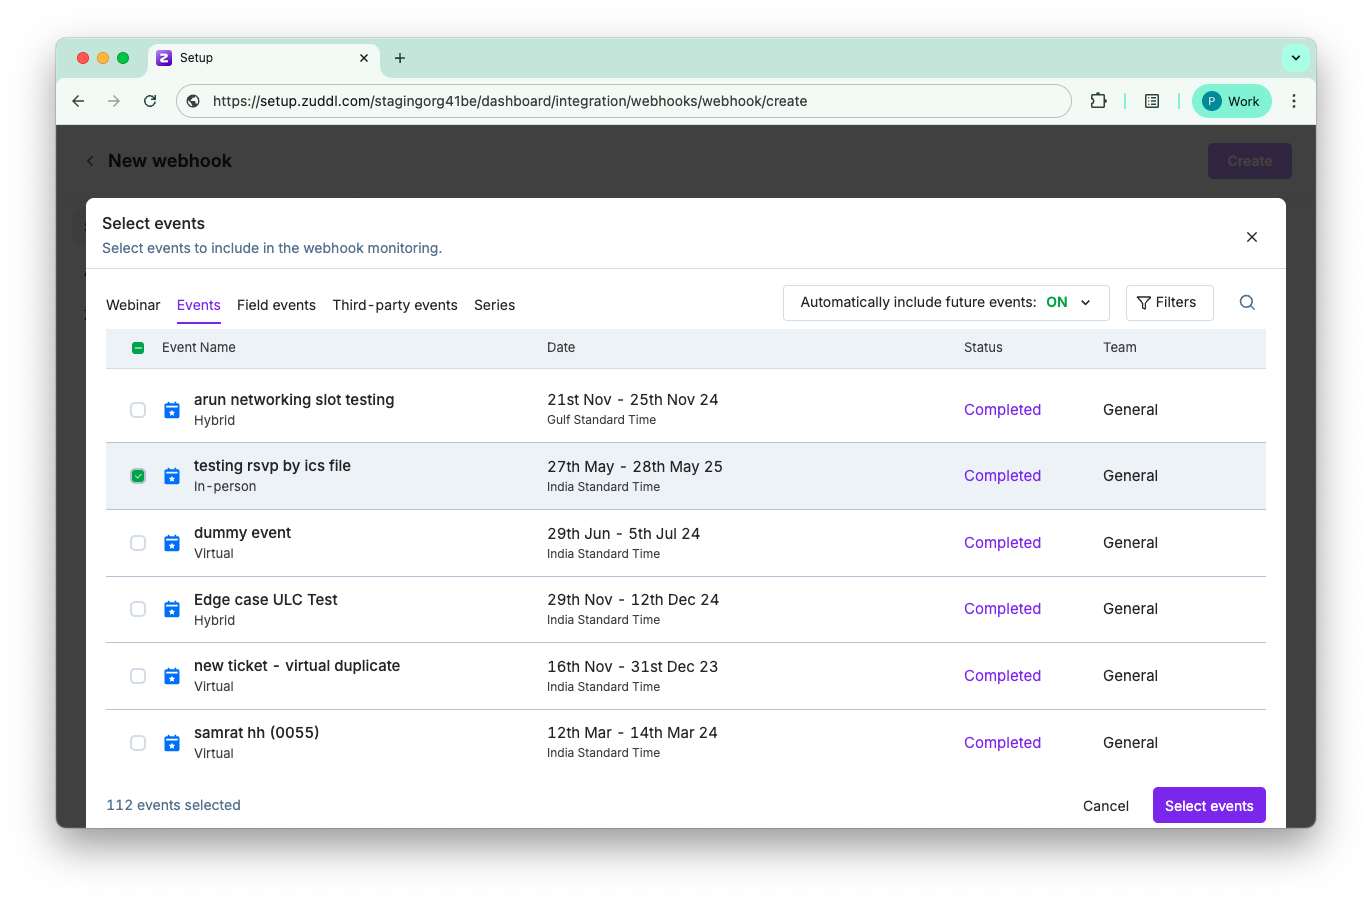
Review the settings and click Create.
This creates the endpoint URL and it appears on the Manage webhooks page. Zuddl starts sending payloads immediately.
Conditions
- If you have selected events, choose at least one event action.
- If you did not select any events, choose at least one org action.
Payload format & signature
The webhook payload format and signature are shown below:
Webhook payload
{

  "webhook_version": "2025-07-01",

  "org_id": "org_123",

  "event_id": "evt_456",

  "action": "registration.approved",

  "timestamp": "2025-07-18T09:21:34Z",

  "data": { ... }

}
Refer to the sample payload of all the supported actions.
Webhook Signature
Zuddl signs each request with your secret key and sends the signature in the Authorization header. If you add a custom Authorization header, the signature is sent in the X-Zuddl-Signature header instead. Recreate the signature on your server with:
signature = base64(hmac_sha256(secret_key, raw_request_body))Only process the payload if digests match.
Custom headers
Custom headers let your endpoint verify that a request came from Zuddl, and pass API keys, tokens or routing tags your systems need. They are sent on every delivery from the webhook, including retries.
Up to 3 headers per webhook.
Header names can be up to 128 characters and must use standard header characters (letters, numbers and
-, for example). Names must be unique within a webhook; case is ignored.Header values can be up to 2,048 characters and must be printable ASCII. Spaces at the start or end are trimmed.
Setting Authorization replaces the default signature in that header. The signature is then sent in X-Zuddl-Signature.
Removing all headers and saving the webhook clears them.
Reserved headers
The following headers are managed by Zuddl and cannot be added or overridden: Content-Type, Content-Length, User-Agent, Host, Transfer-Encoding, Connection, Expect, TE, Upgrade, Keep-Alive, Proxy-Authorization and X-Zuddl-Signature. They control how the request is delivered and how its signature is verified, so changing them could break delivery or verification.
Managing webhooks
To any given endpoint URL, you can take the following actions:
Edit: edit the webhook settings. Every field configuration is editable. No data is lost when you edit.
Delete: Delete a webhook permanently
Inactive: Pause or disable the webhook
Limits & retries
Limit | Value |
Max webhooks/org | 20 |
Delivery rate | 1000 events/min/webhook |
Latency target | ≤ 3 s |
Retry policy | 10 attempts in ~12 hrs (exponential back-off)
|
Webhook Failure and Retry Logic
If a webhook URL takes longer than 4 seconds to respond, the request is considered a failure. In such cases, the payload will be automatically retried by Zuddl to ensure the data reaches the destination.
Avoiding duplicate webhook payload
To avoid receiving duplicate webhook payloads, ensure that any processes before responding to the webhook are asynchronous. This means that the webhook should not be part of any synchronous workflow that requires waiting for responses before acknowledging the webhook.